AI Governance & PDPA Compliance
A practical, one-day programme for Malaysian businesses whose teams are already using AI. Understand what the law asks of you, and leave with your own written AI use policy drafted — not a folder of slides.
At a glance
Your Team Is Already Using AI. Your Policy Probably Says Nothing About It.
Most Malaysian companies discovered AI through their own staff, not through a plan. That gap between what people are already doing and what the organisation has actually approved is where the risk sits.
Staff Are Already Pasting Data In
Customer lists, salary tables, contracts, medical records — copied into free AI chatbots to "just summarise this". Usually with good intentions, almost always without approval, and often without anyone knowing where that data ends up.
The Rules Changed in 2025
Amendments to Malaysia’s Personal Data Protection Act came into force in June 2025, introducing mandatory Data Protection Officer appointment, breach notification, and data portability obligations. Many SMEs have not revisited their practices since.
A Written Policy Is the Practical Fix
There is no requirement to ban AI — and banning it does not work anyway. What works is a clear, written policy on what may and may not go into these tools, backed by staff who understand the reasoning. That is what this day produces.
Six Blocks. You Leave With a Written Policy.
This is not a lecture on regulation. Roughly half the day is spent drafting your own organisation’s AI use policy in the room, using a working template, so the output is a document you can actually take to your management team.
The Exposure You Cannot See
Establish, in plain language, what actually happens to information once it is typed into an AI tool — and where the everyday exposure in a Malaysian business really comes from.
The Exposure You Cannot See
Establish, in plain language, what actually happens to information once it is typed into an AI tool — and where the everyday exposure in a Malaysian business really comes from.
The People Who Sign Off, and the People Who Implement
This programme works best when a decision-maker and an implementer attend together — the policy then leaves the room with both authority and a practical owner.
Business Owners & Directors
Understand the organisation’s exposure well enough to make a decision, and approve a policy you actually understand
Data Protection & Compliance
Extend existing PDPA practice to cover AI tools, with documentation that stands up to scrutiny
HR & Admin Leads
Handle employee and candidate data responsibly when AI is used for screening, drafting and summarising
IT & Operations Managers
Turn an approved policy into real controls — tool selection, settings, access and incident handling
A Document, Not Just Notes
Every participant leaves with drafted work in hand, plus the reasoning to defend it to their own management.
- A drafted AI use policy scoped to your own organisation, ready to refine and approve
- A plain-language understanding of PDPA obligations when AI processes personal data
- Clarity on the June 2025 amendments — DPO appointment, breach notification and data portability
- A vendor assessment checklist to use before signing with any AI supplier
- An outline incident response process for AI-related data exposure
- A staff briefing plan so the policy is understood rather than ignored
- Familiarity with the AIGE principles and Malaysia’s likely regulatory direction
- A review schedule to keep the policy current as the rules develop
Delivered in Your Room, at Your Pace
Photographs from AISynergy training sessions. This programme runs the same way — in-house, practitioner-led, small enough that every participant can raise the awkward questions their own organisation actually faces.
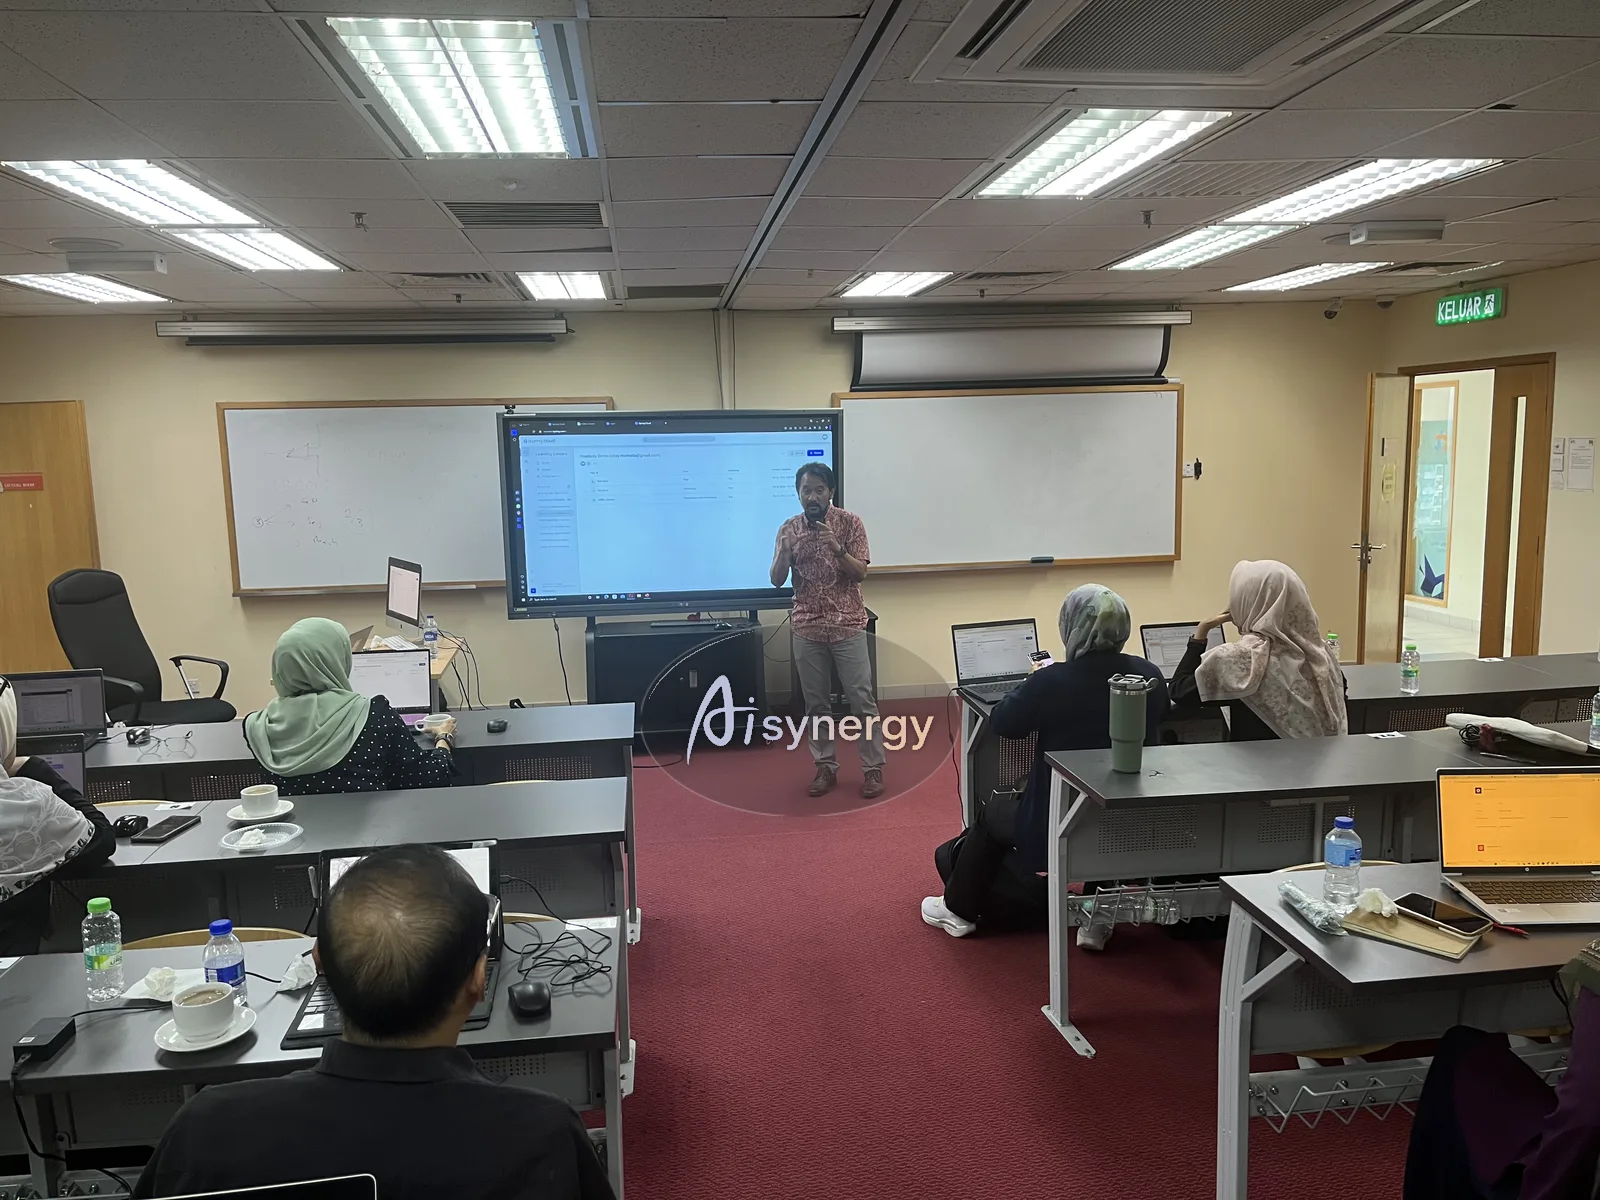
Worked through live, with the room following
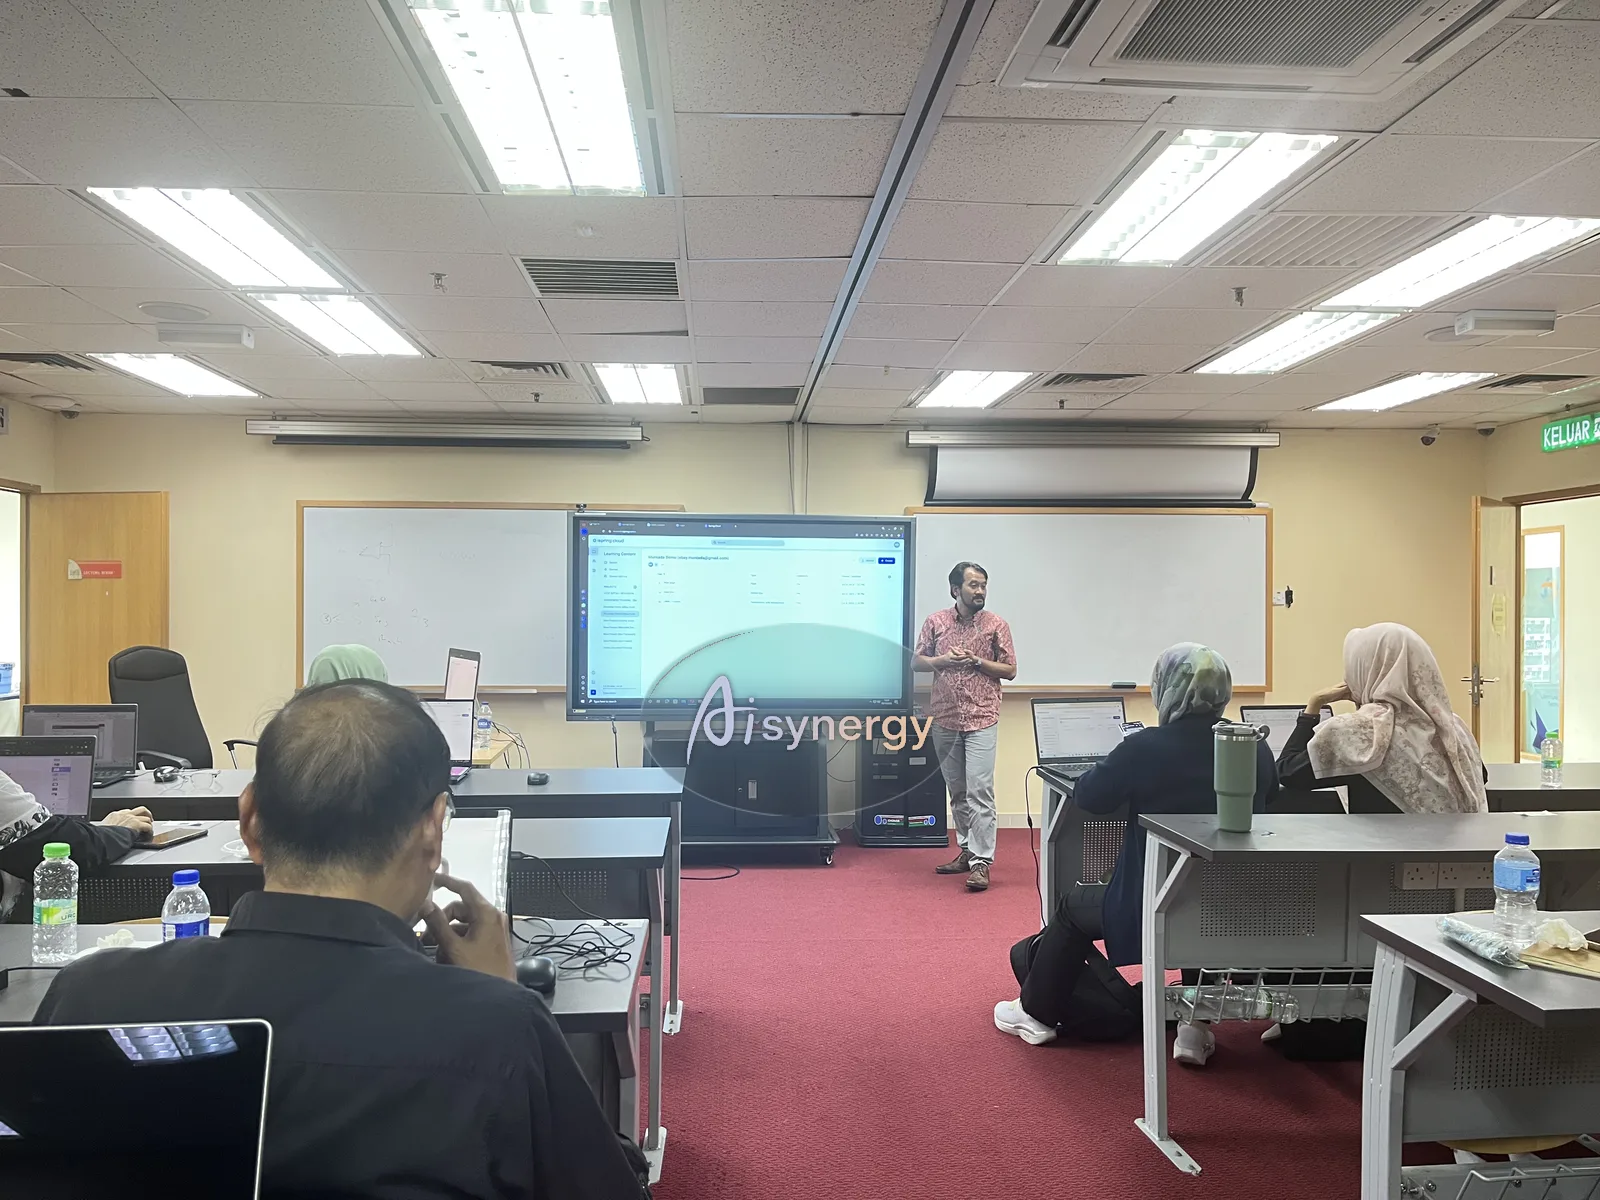
Delivered in the client’s own training room
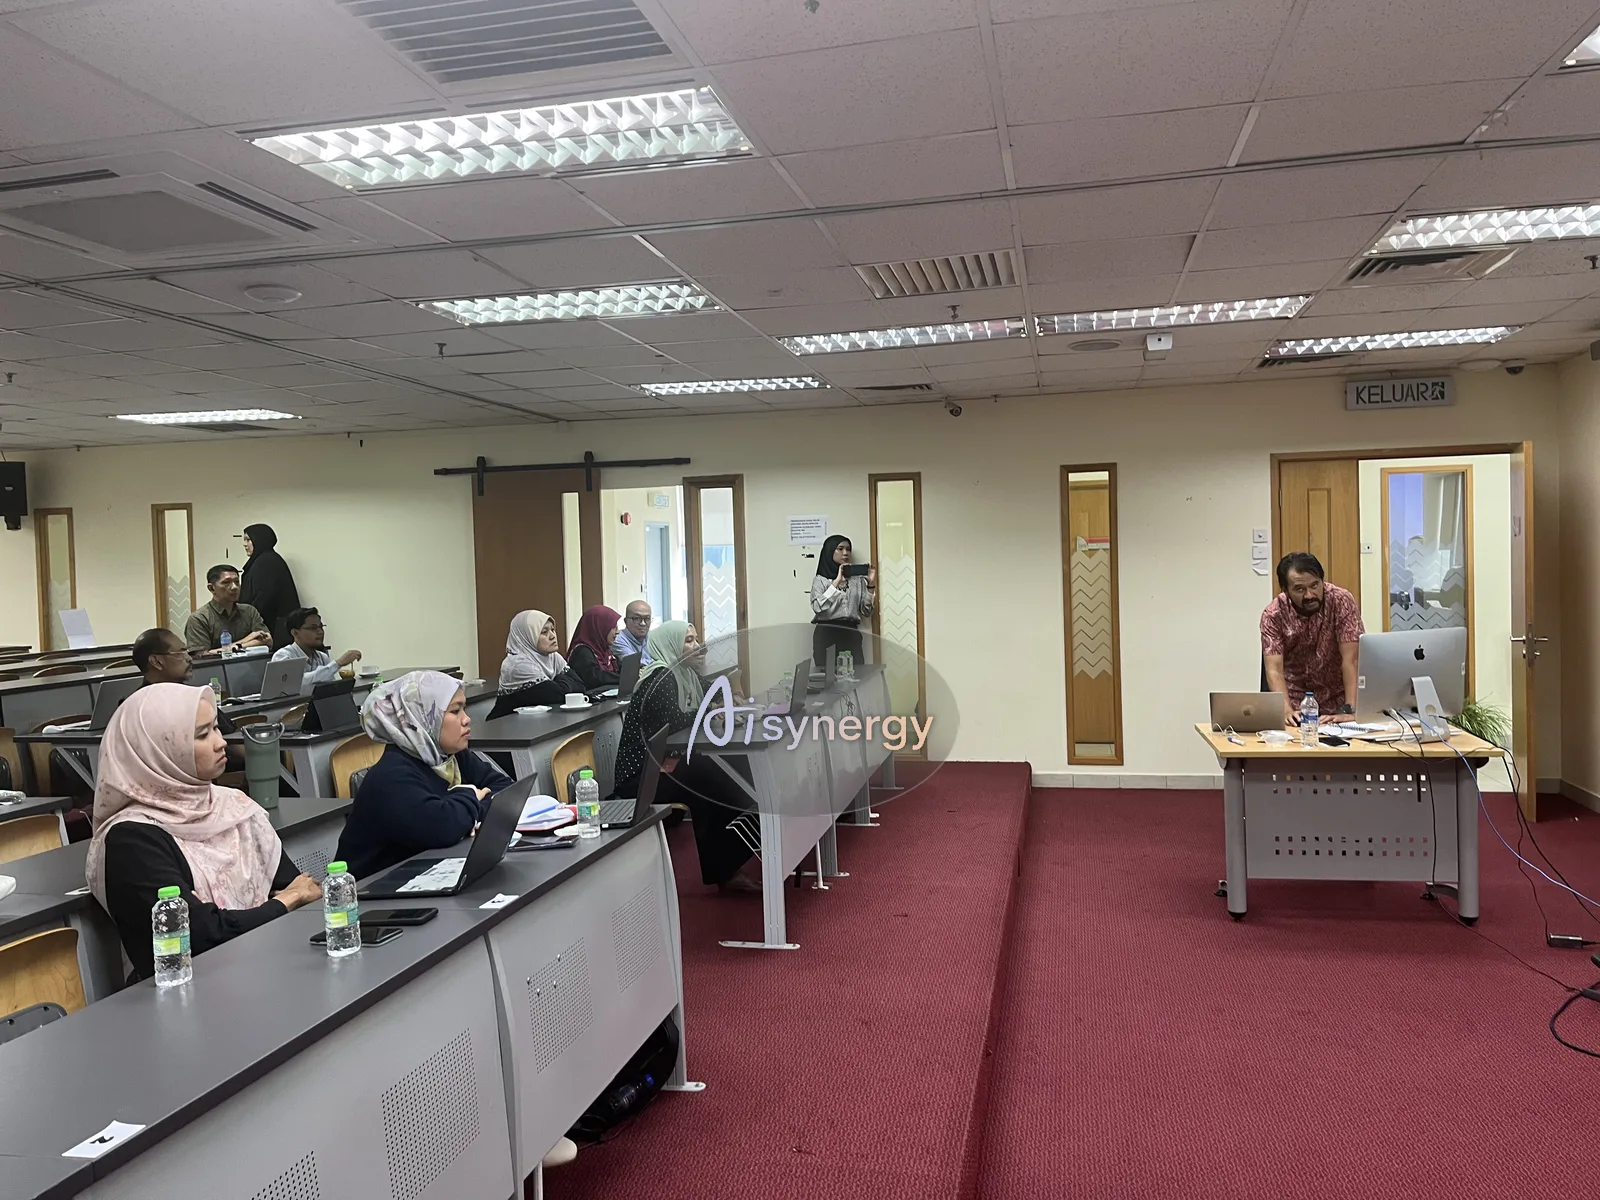
Kept small enough for everyone to be heard
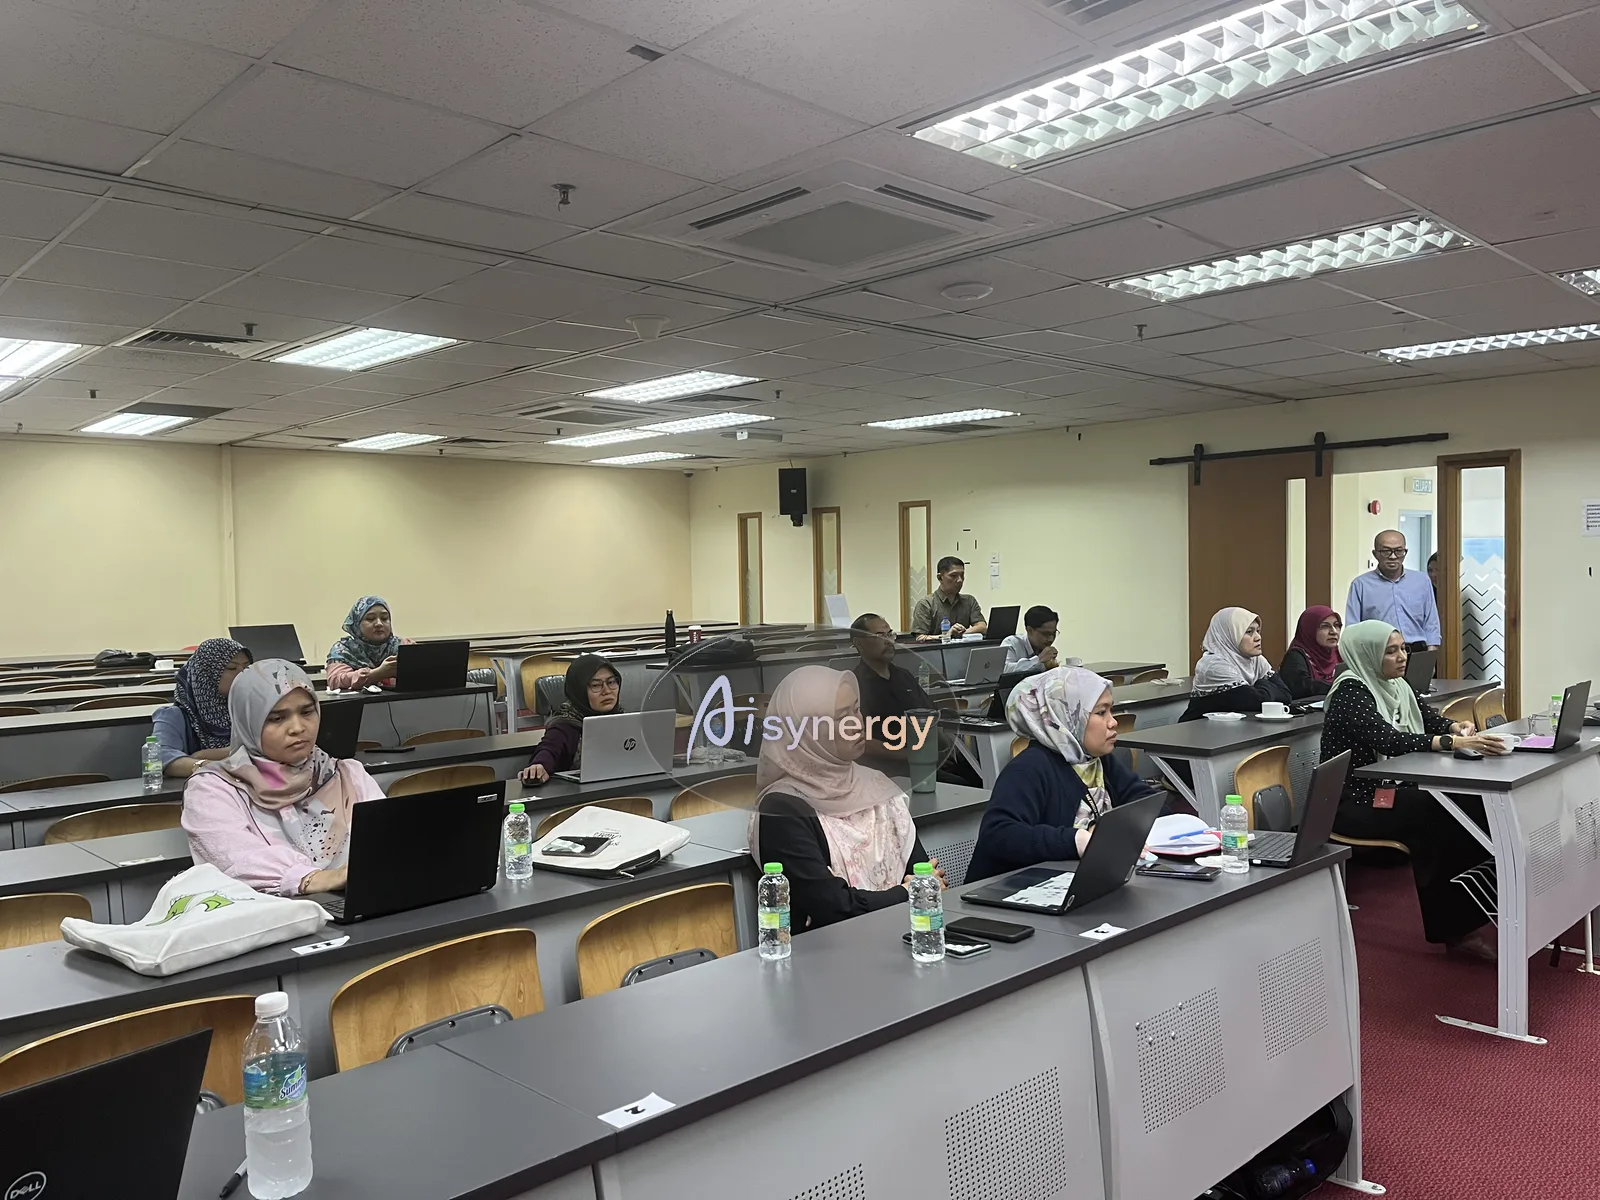
Departments working through it in the same room
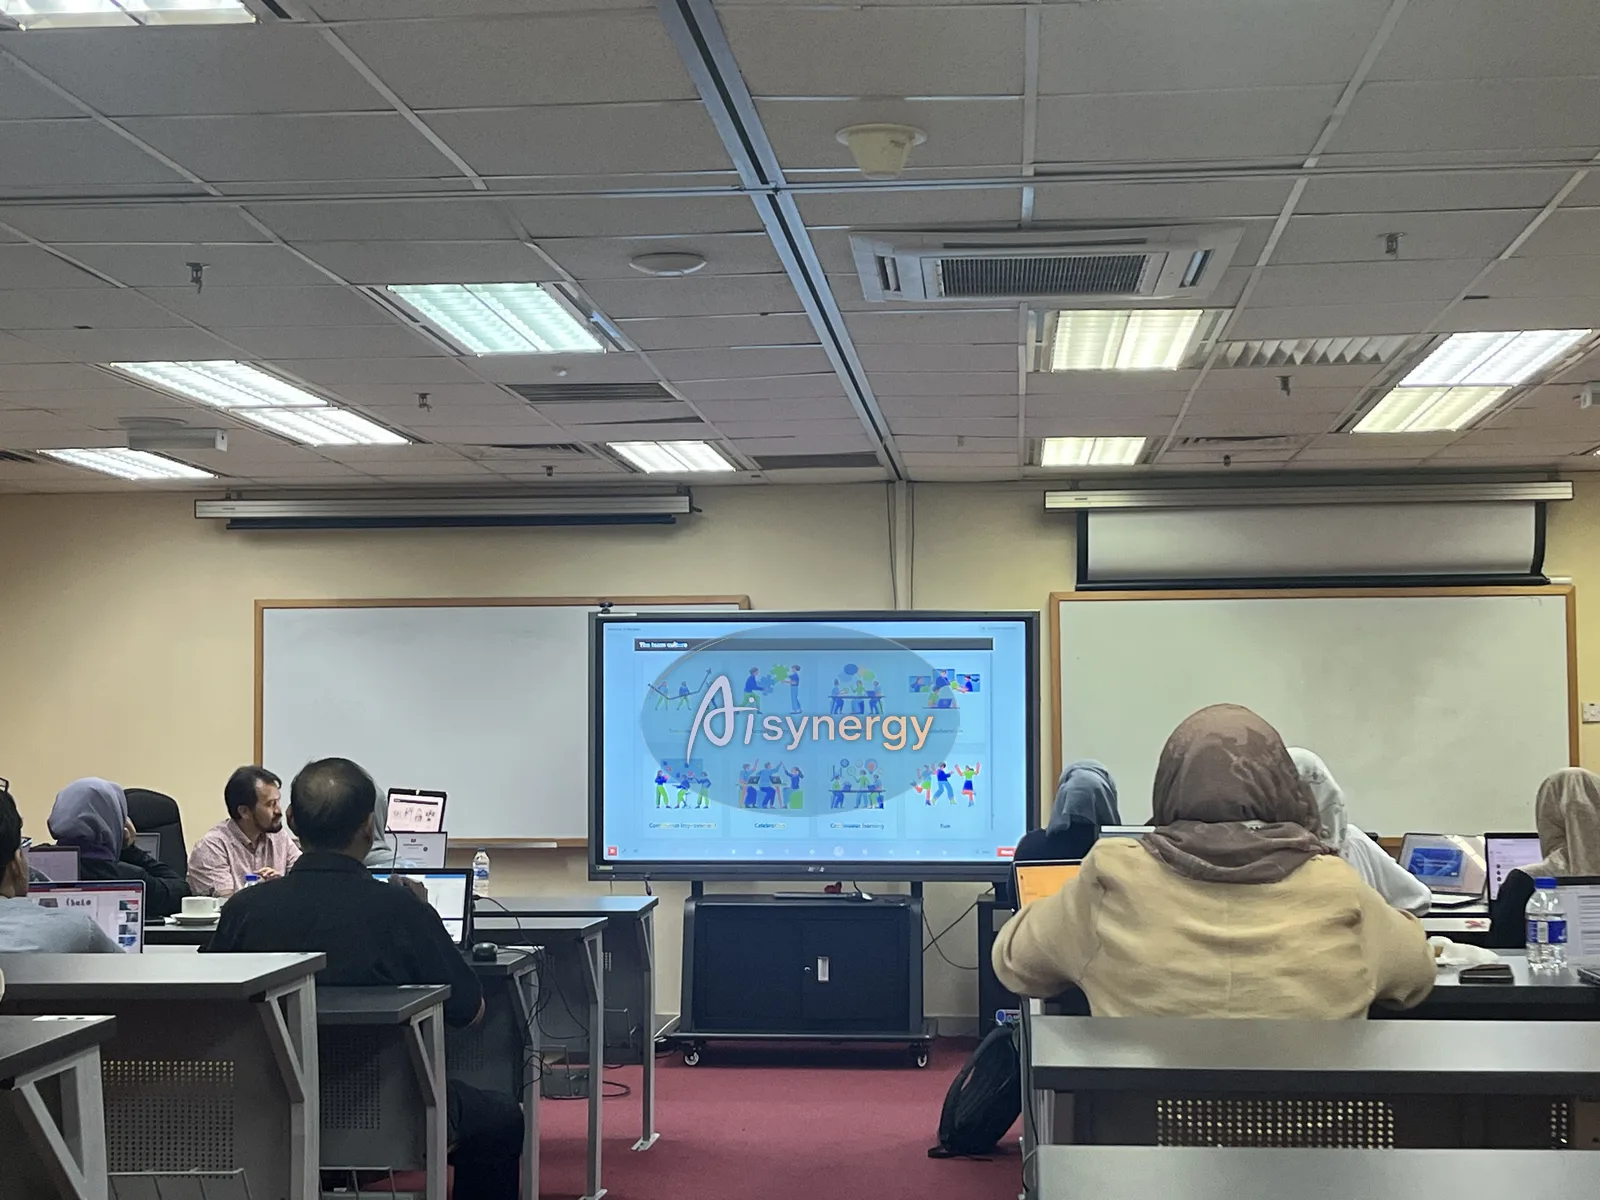
Shown on screen, then tried on their own laptops
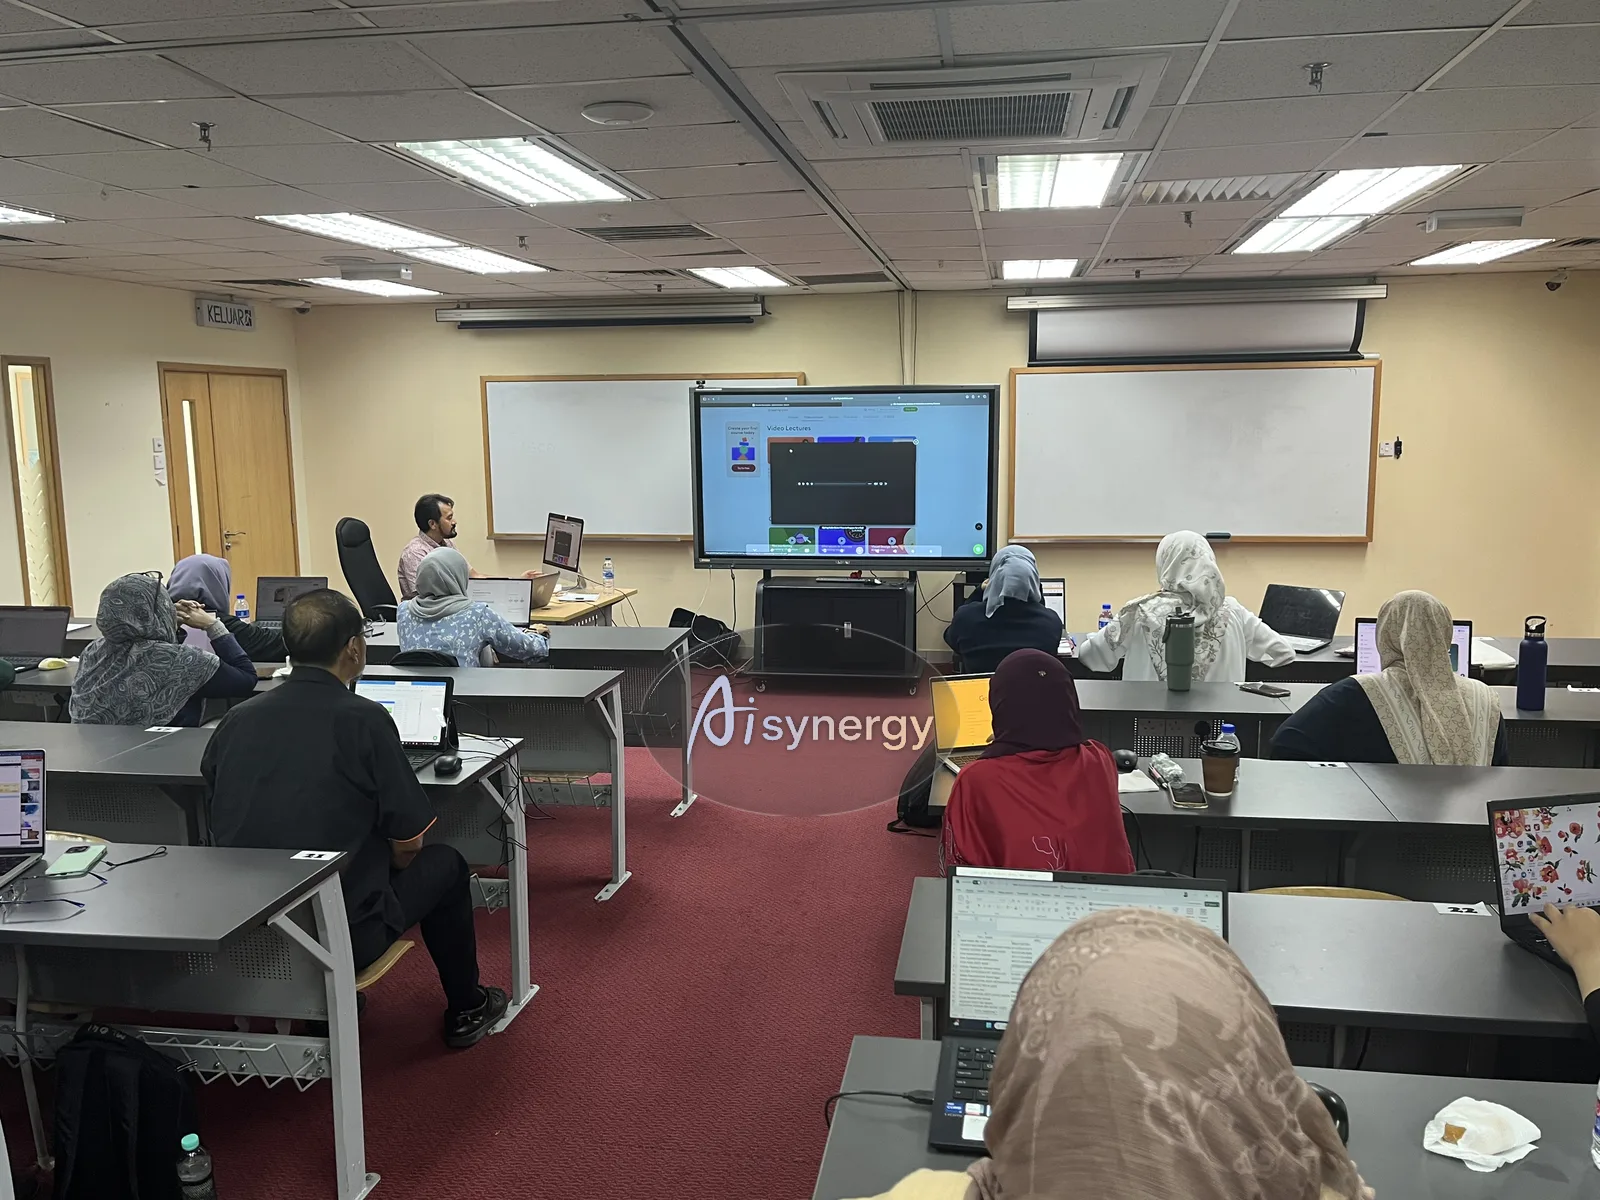
Everyone on a laptop, working along
Claimable Training, Plus Budget 2026’s Extra Deduction.
This programme is claimable under the HRD Corp SBL-Khas scheme for registered Malaysian employers. Budget 2026 also introduced a 50% additional tax deduction for MSME spending on AI and cybersecurity training, administered through TalentCorp — ask us and we will point you to the current terms.
- Training Provider Reg. 202403037477
- Full supporting documents provided for HRDC claim submission
- Attendance records and trainer profile included
- Dedicated guidance for the HRDC claim process
- Delivered in-house at your premises, or as a public session
Write the Policy Before You Need It.
Available as an in-house programme at your premises, or as a scheduled public session. Talk to us about dates.
+603 6087 5252 · aisynergy.my
This programme provides general guidance and practical templates for building internal AI governance practice. It is training, not legal advice, and it does not create a solicitor-client relationship. Regulatory requirements change and vary by sector — organisations should confirm their specific obligations with a qualified legal adviser before relying on any policy produced during the session.
© 2026 AISynergy Malaysia · Registration No. 202403037477